Sales: +91 9600 70 3224
- Support


Every privileged session proxied, recorded and time-bound, with the password injected and revoked by the platform.
Your administrators need access to servers, databases and Kubernetes. Your auditors need proof of everything that happened. Your credentials need to stay out of everyone's hands. Akku PAM does all three through two components: AkkuArka, which generates a fresh credential for every session, and AkkuReka, the proxy every privileged connection passes through. The user connects and works normally. They never see the password, because it was injected at the protocol layer and revoked the moment the session closed.
Privileged access management is the practice of controlling and recording the access that administrators, engineers and contractors hold to the systems that run a business: servers, databases, network devices, cloud consoles. It exists because those accounts can change or destroy anything, and because a shared root password with no record of who used it is indefensible to an auditor and untraceable after an incident. Akku does it by putting a proxy between the person and the target. Identity, device, location, time and role are checked before a session opens, an approval can be required, and the credential the target accepts is generated for that session alone and destroyed at the end of it. Everything that happens inside the session is recorded, and every command is logged.
Every privileged connection through one proxy.
SSH, RDP, MySQL, PostgreSQL, MongoDB, Kubernetes and web targets are all reached through AkkuReka. Sessions are recorded as video, SSH commands and database queries are captured in full, and an administrator can watch a session live and end it mid-connection. The target system never knows the real user's identity.
Learn more
Per-session credentials, and a vault for what has to be stored.
AkkuArka generates a credential for each session, injects it into the proxy at the protocol layer, and revokes it when the session closes. Nothing to rotate afterwards and nothing left behind. Where a standing credential has to exist, SSH keys, API keys, database logins, application secrets, AkkuArka's vault holds it under AES-256-GCM, reachable only through the AkkuArka API and never by a person.
Learn more
No standing access, and nothing opens without passing policy.
A request is evaluated on device posture, location, IP reputation, time of day, role and any active JIT window before a session opens, with MFA stepping up when something looks off. Where approval is enabled the session stays pending until an approver acts. Roles scope what a session can reach: which targets, which protocols, which hours, how long. And a permitted-command list limits what runs inside the session, with blocked attempts logged as failed.
Learn more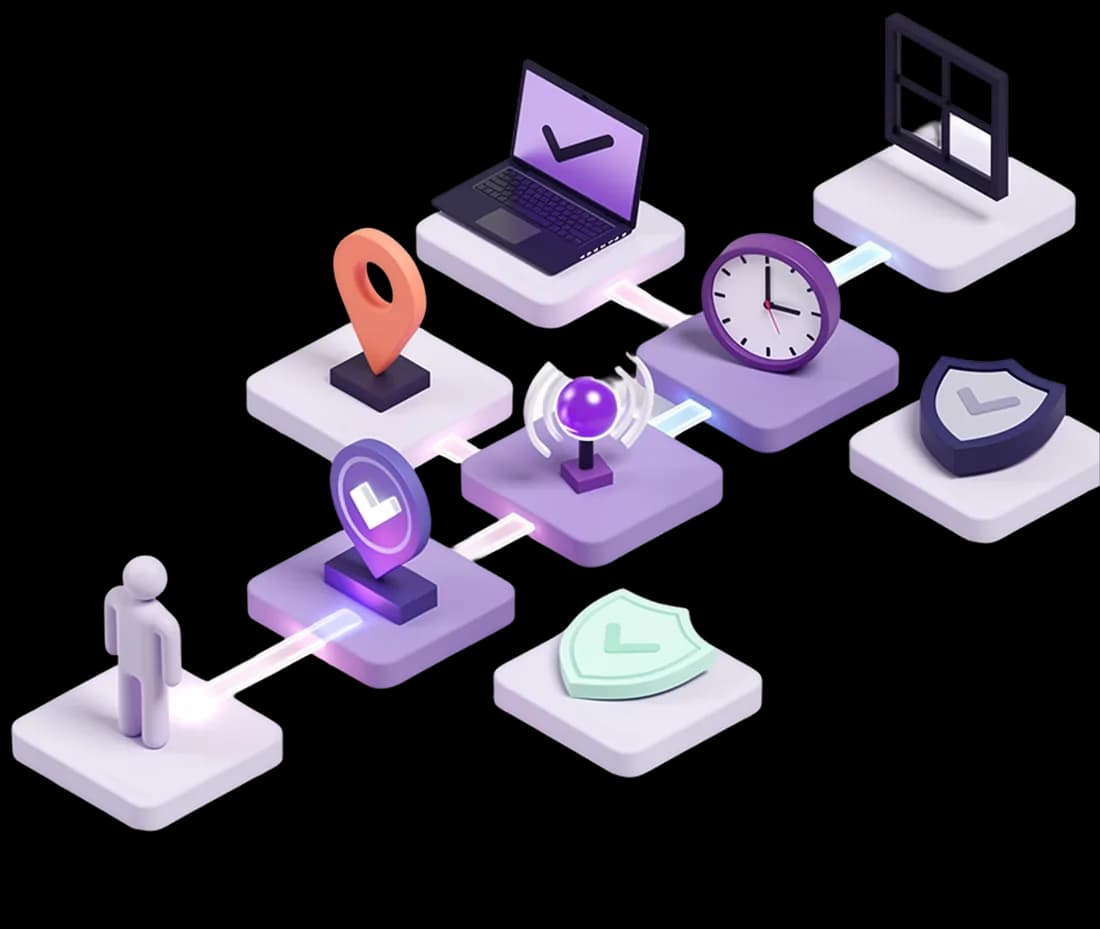
Admin consoles and SaaS dashboards, in an isolated browser Akku controls.
A privileged web session runs in a throwaway browser on Akku's gateway rather than on the user's machine. Akku signs them in with a credential from the vault and streams the session to their screen. Downloads are blocked by default and copying out to the local clipboard is blocked by architecture, because there is no clipboard bridge to cross. The session is recorded as video, with the sign-in step kept out of the recording. Nothing to install.
Learn more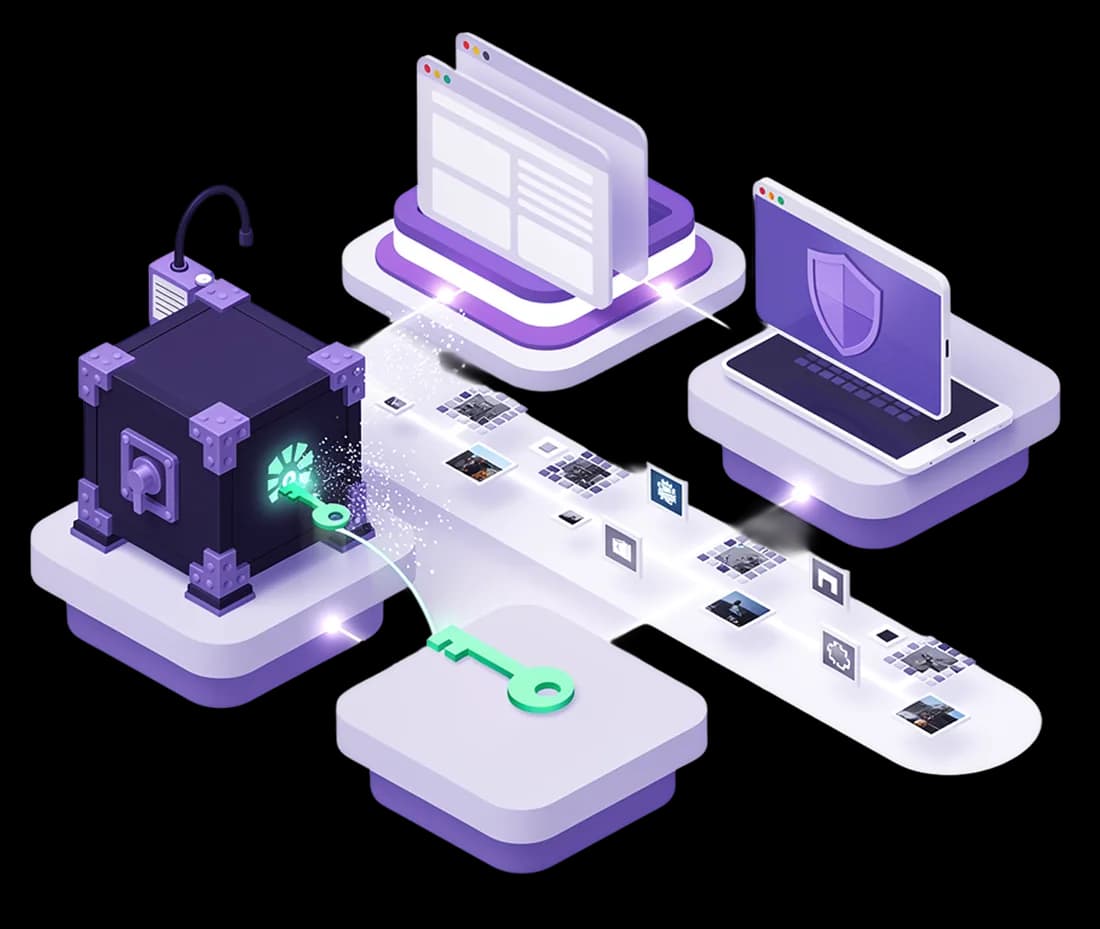
One worker per network, outbound only, no inbound rule anywhere.
Isolated networks are where most PAM tools ask for either a full deployment inside every zone or firewall rules a security team will never approve. AkkuArka and AkkuReka stay central. A lightweight worker sits inside each isolated network and makes only outbound connections out to them. Adding a zone takes minutes and your firewall stays exactly as it is.
Learn more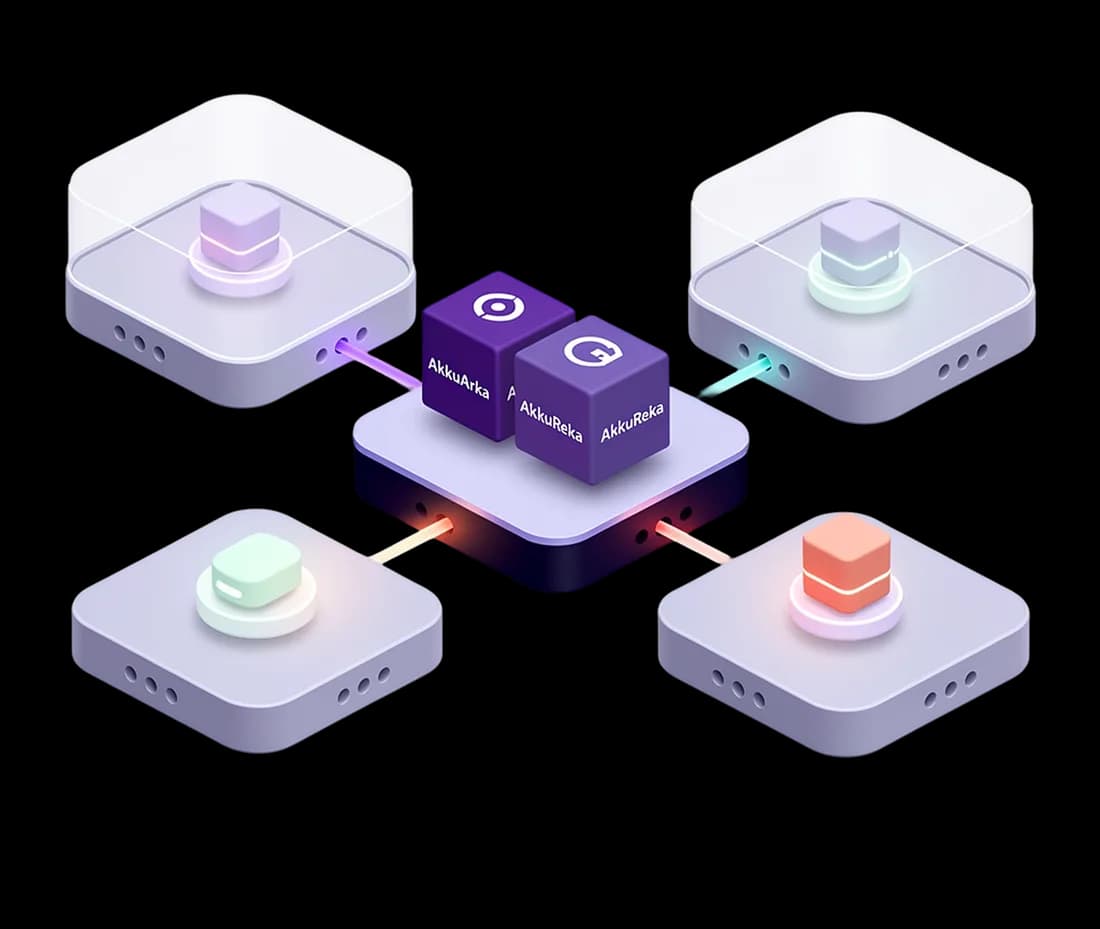
Every session request, approval, denial, open and close. Every credential generated, injected and revoked. Every MFA prompt, geo block and IP block. Every role assignment and policy change. Each entry carries the actor, the target, the session it belongs to, the outcome, the source IP and the resolved location, and the log is append-only, so records cannot be modified or deleted. Export as JSON or CSV for an auditor, or pull it through the API into your SIEM.
A certificate authority for issuing, renewing and revoking certificates and governing certificate-based authentication. A file vault with per-tenant keys, time-limited sharing and an approval workflow for release. Organisations, which scope access, policy and delegated administration across business units. My Access, where a person sees the systems they are entitled to, their own active sessions and requests, and anything pending their approval, included at no additional cost. Bulk import for onboarding a large estate of systems and accounts at once.